 ██████╗ ███╗   ███╗███╗   ██╗██╗███████╗██████╗ ██╗      ██████╗ ██╗████████╗
██╔═══██╗████╗ ████║████╗  ██║██║██╔════╝██╔══██╗██║     ██╔═══██╗██║╚══██╔══╝
██║   ██║██╔████╔██║██╔██╗ ██║██║███████╗██████╔╝██║     ██║   ██║██║   ██║
██║   ██║██║╚██╔╝██║██║╚██╗██║██║╚════██║██╔═══╝ ██║     ██║   ██║██║   ██║
╚██████╔╝██║ ╚═╝ ██║██║ ╚████║██║███████║██║     ███████╗╚██████╔╝██║   ██║
 ╚═════╝ ╚═╝     ╚═╝╚═╝  ╚═══╝╚═╝╚══════╝╚═╝     ╚══════╝ ╚═════╝ ╚═╝   ╚═╝
The complete pentest workflow in a single pane of glass.
From OSINT/Recon to Reporting — one tool, one terminal, zero context switching.
WHAT IT IS
OmniSploit unifies every phase of an engagement behind one operator console — subprocess orchestration, live SSE terminals, an encrypted credential vault, engagement scoping, CVE enrichment, and reporting — so you never leave the tool to change context.
CAPABILITIES
RECON + OSINT // recon
nmap discovery, masscan, naabu, Shodan, and an OSINT suite — crt.sh, RDAP, whois, Wayback, theHarvester/amass/subfinder — with Review & Promote and an Entity Map.
INVENTORY + MAPS // inventory
Asset inventory rebuilt from disk, Network Map, Cloud Inventory and an Entra/Azure Cloud Map, saved views — all on one Cytoscape layout engine.
WEB // web
Crawl Map: katana → link graph with orphans, IDOR and hub hints, plus opt-in OWASP ZAP DAST.
ENUMERATION // enum
AutoRecon with live SSE streaming, gowitness screenshots, a results file tree, and a Next-Steps command parser.
VULNERABILITY // vuln
Nuclei (profiles P1–P23 + DAST fuzzing templates), Nikto, WPScan, testssl, SQLMap, FFUF, MCP Audit, and opt-in OpenVAS.
AUTO-PIPELINE // engine
Auto-chained 22-phase web-app pipeline over an Engagement Asset Graph — tool output → next input, stage approval gates, per-target throttle, 7 native omni-* probes.
EXPLOIT + BRUTE // exploit
impacket suite, NetExec, Responder, Coercer, NTLM relay / ADCS (certipy), opt-in Metasploit RPC, plus hashcat/john and Hydra.
CREDENTIAL VAULT // lateral
AES-Fernet SQLite store; a random master key wrapped per user under PBKDF2(login password), held in memory only. A picker wires creds into NetExec / impacket / Responder jobs.
BLOODHOUND CE // ad
Collect, run Cypher, and render the graph in Cytoscape — prebuilt queries, mark-owned, AD Health, AD Map, PrivHound paths.
CLOUD // entra · aws · k8s
ROADtools, TeamFiltration, Entra recon, AzureHound, CloudFox, Prowler, ScoutSuite, kube-bench/kubescape and more.
DELIVER + C2 // deliver
Engagement File Server (basic auth over TLS, uploads → loot), transfer one-liners, PEAS over SSH/SMB, and opt-in Sliver C2.
SOCIAL ENGINEERING // phish
Opt-in Gophish campaigns (+ Postfix relay) and Evilginx, scope-gated like every launch.
ATT&CK // emulate
Coverage map derived from tools and CWEs, a threat-actor emulation overlay, and opt-in Atomic Red Team.
ENRICHMENT + REPORT // report
CVEs enriched from CISA KEV, EPSS, NVD and offline ExploitDB/MSF metadata. OmniReport renders HTML · PDF · DOCX · PPTX · CSV · XLSX.
SCREENSHOTS
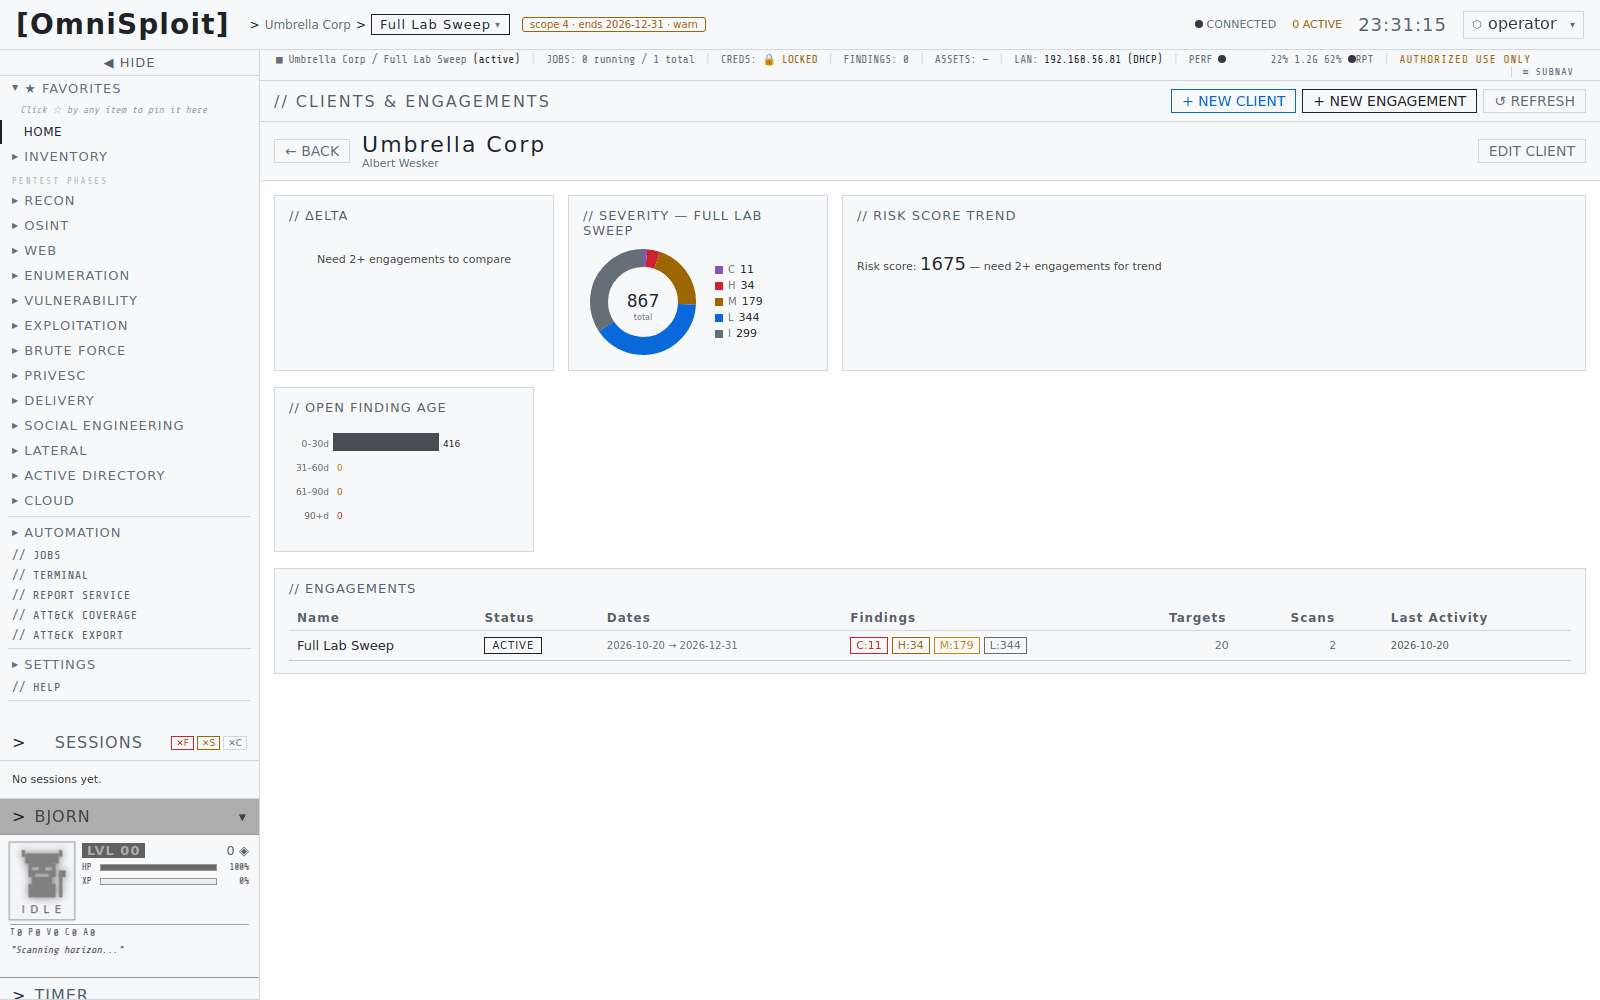
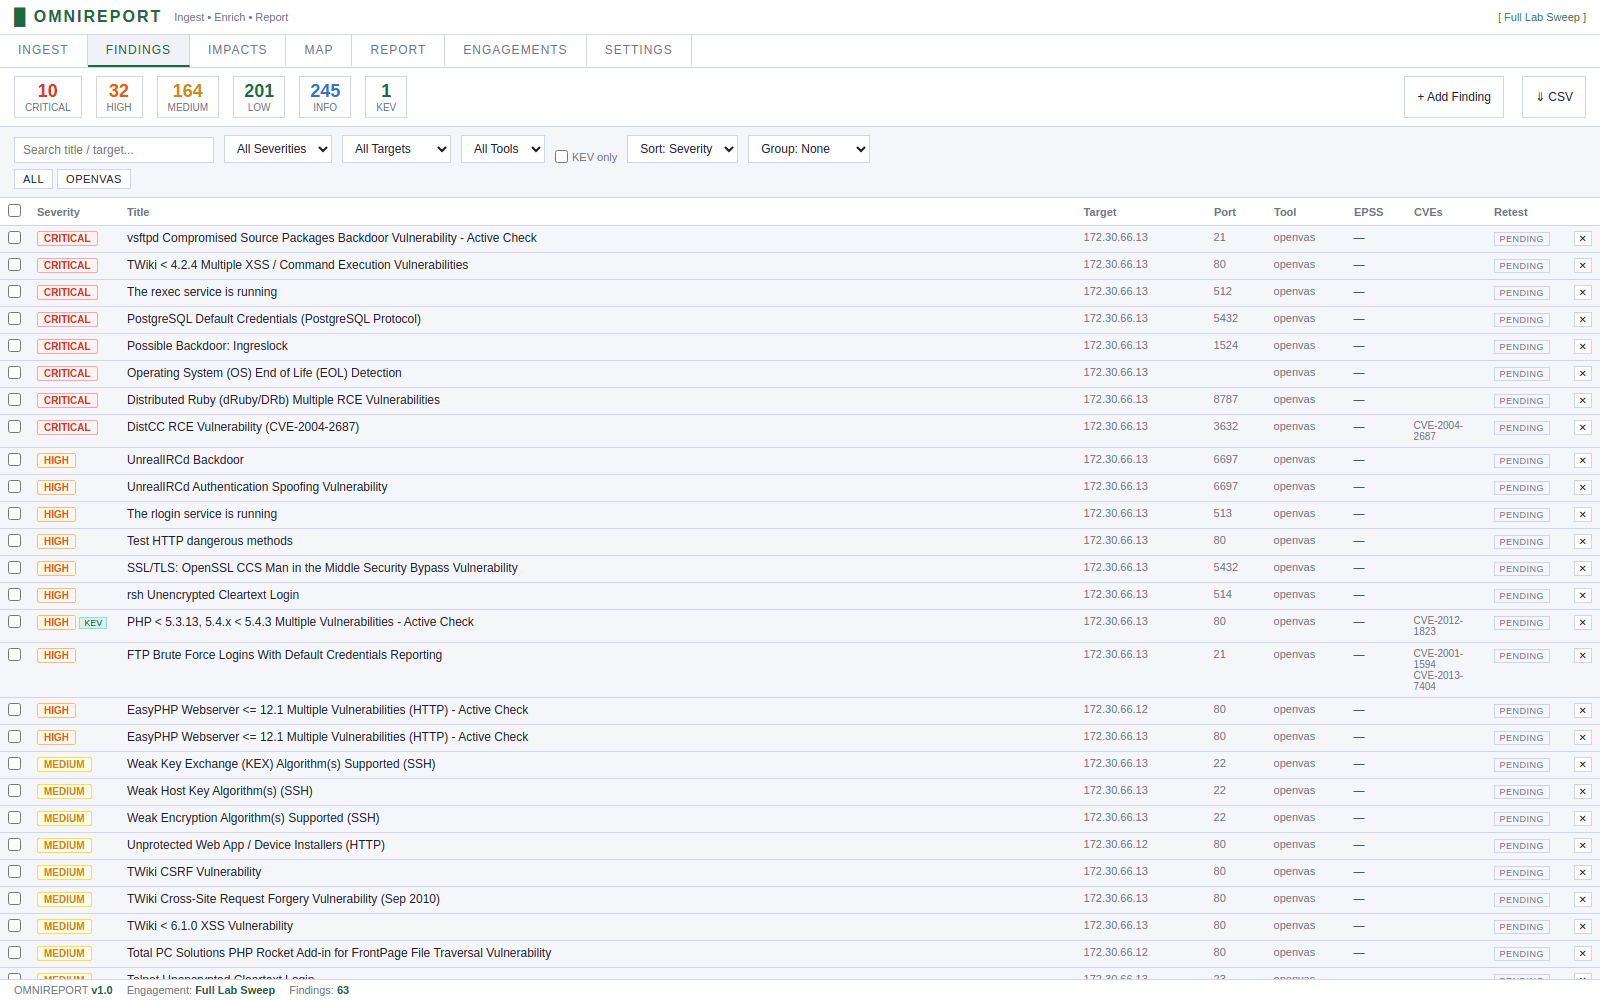
Captured from the internal CTF lab engagement (fictional client, lab-only addresses).
UNDER THE HOOD
- Multi-tenant engagements — client CRUD, per-engagement scoping, overtime metrics
- Live SSE terminals + interactive PTY shell over Socket.IO
- Importers: Nessus, OpenVAS, Qualys, Nexpose, Burp, ZAP, Nikto, nmap, NodeZero, Cavelo, PurpleKnight, CSV
- All subprocess calls server-side, shell=False, engagement-scoped output
- require_in_scope() on every network-facing launch + scope audit log
- JOBS queue with a concurrency cap — no more OOM bursts
- PBKDF2 auth, admin/operator roles, forced first-login password change, CSRF origin checks
- Findings dedup + 9-state lifecycle / SLA triage overlay
- Engine has no Docker create rights — locked socket proxy + stackctl agent
- Secrets are files, never environment variables
ARCHITECTURE
Caddy is the only service on host interfaces. The engine reaches Docker only through a locked proxy on an internal network; optional stacks are opt-in compose overlays.
  operator browser (SPA · SSE · Socket.IO PTY)              in-scope targets
         │ HTTPS :443 console · :5001 reports                │ :8443 files
  ┌──────▼───────────────────────────────────────────────────▼──────────────┐
  │ caddy · TLS (self-signed / Let's Encrypt / Cloudflare) · operator ACL   │◀── tls-watchdog
  └──────┬─────────────────────────┬─────────────────────────┬──────────────┘
         │                         │                         │
  ┌──────▼──────────────┐   ┌──────▼──────────────┐   ┌──────▼──────────────┐
  │ omnisploit engine   │──▶│ omnireport          │   │ delivery            │
  │ Flask+SocketIO 5000 │   │ SQLite findings     │   │ dufs File Server    │
  │ job_gate · scope    │   │ PDF DOCX PPTX XLSX  │   │ off until START     │
  │ auto-pipeline · EAG │   └─────────────────────┘   └─────────────────────┘
  └──────┬──────────────┘                         edge network
         │
         ├──▶ dockerproxy    ctrl net (internal) · start/stop named containers only
         ├──▶ stackctl       enables / disables optional stacks
         ├──▶ volumes        results/<eng> · state (vault) · reports
         ├──▶ opt. stacks    BloodHound · OpenVAS · ZAP · Metasploit · Sliver
         │                   Gophish · Evilginx · HackTricks · Atomic Red Team
         ├──▶ feeds          CISA KEV · EPSS · NVD v2 · Shodan · OSINT sources
         └──▶ targets        subprocess (shell=False), engagement-scoped
                             bridge net, or LAN overlay macvlan lan0 for L2
One launch: request → Caddy (TLS + ACL) → auth / CSRF / scope gate → job_gate queue →
subprocess → results/<engagement>/<target>/scans/ → live SSE → findings parsed read-only,
enriched, synced to OmniReport → report.
REQUIREMENTS
Measured on a running lab deployment (2026-10-26) unless marked observed; default Docker path.
| Resource | Core stack | Notes |
|---|---|---|
| CPU / arch | x86_64 only | Pinned binaries are linux_amd64. Core count not benchmarked; hashcat/john are the CPU-heavy jobs. |
| RAM | ≥ 8 GB host | Engine idles ≈ 0.5 GB; OmniReport capped at 2 GB. A 7 GB host was OOM-killed (observed) by a parallel scan burst — use the JOBS cap / OMNISPLOIT_ENGINE_MEM. |
| Disk | ≥ 40 GB free | Engine image 19 GB + ≈ 9 GB build cache per rebuild (observed). Keep ≥ 15 GB free before each rebuild. |
| GPU | optional | hashcat is CPU-only unless you pass --gpus all (NVIDIA runtime). |
| Network | internet at build | apt, pip/pipx, go install, GitHub releases, Nuclei templates. L2 tools need the LAN overlay. |
| Software | Docker + Compose v2 | sudo, git, openssl, python3, curl. The installer adds Docker if missing. |
| Optional stack | RAM caps | Disk |
|---|---|---|
| BloodHound CE | 4 GB + Neo4j 2 GB + Postgres 512 MB | ≈ 1 GB images + graph volume |
| OpenVAS | ≈ 8 GB of caps (4–6 GB used scanning) | ≈ 9–10 GB images + ≈ 39 GB volumes measured (DB 26.5 GB, SCAP 10.9 GB) |
| ZAP · MSF · Sliver | 2 GB each | ZAP 3.8 GB, Sliver 2 GB images |
| Gophish · Evilginx | 512 MB each (+256 MB relay) | small |
| HackTricks | 3 GB builder (index ≈ 4.5 GB) | ≈ 0.7 GB builder + source |
DEPLOY
| Method | Command |
|---|---|
| Scripted | OS_CERT_MODE=selfsigned OS_DOMAIN=box.lan deploy/install.sh --non-interactive --deploy |
| One-shot | deploy/up.sh — Docker + secrets + self-signed + build + up |
| Manual | deploy/init-secrets.sh && sudo docker compose build && sudo docker compose up -d |
| Per-engagement | deploy/deploy.sh <engagement> [up|down|build|logs] — isolated volumes |
| Optional stacks | deploy/<stack>.sh enable|disable|status — bloodhound, openvas, zap, msf, sliver, gophish, evilginx, hacktricks, atomic (or SETTINGS › Optional stacks) |
| LAN overlay | deploy/lan.sh enable --iface <if> --dhcp — Responder / mitm6 / L2 |
| OmniReport only | deploy/omnireport-standalone.sh [--tls|--down] |
| Bare metal (dev) | ./start.sh [--port N] [--no-omnireport] → http://localhost:5000 |
No cloud one-click templates and no CI/CD pipeline ship with the project — deploy on any x86_64 Linux VM with Docker.
TOOLS
87 registry integrations + extras, verified inside the built image. ⚠ = not in the image.
| Phase | Tools |
|---|---|
| Recon | nmap, masscan, naabu, AutoRecon, bbot, getallurls, asnmap |
| OSINT | theHarvester, amass, subfinder, whois, Shodan API |
| Enumeration | gobuster, feroxbuster, ffuf, gowitness, whatweb, sslscan, dnsrecon, enum4linux, smbclient, snmpwalk, wafw00f, ssh-audit, smtp-user-enum, odat |
| Web | httpx, katana, arjun, interactsh-client, dalfox, SSTImap, graphql-cop, jwt_tool, dnsx, checkdmarc, s3scanner, trufflehog, git-dumper, droopescan, CMSeeK, subzy, phpggc, ysoserial ⚠ |
| Vulnerability | Nuclei (+ fuzzing templates), Nikto, WPScan, testssl.sh, SQLMap, snyk-agent-scan (MCP audit) |
| Exploitation | NetExec, impacket suite, Responder, mitm6, krbrelayx, Coercer |
| Lateral / AD | getTGT / getST / ticketer, certipy-ad, bloodhound-ce-python, bloodyAD, evil-winrm, kerbrute, pypykatz, ldeep |
| Brute force | hashcat, john, hydra, cewl, crunch, wordlists |
| Privesc / post | linPEAS / winPEAS, PrivHound, sshpass, sshuttle, proxychains4, socat |
| Cloud | roadrecon, roadtx, TeamFiltration ⚠, AzureHound, CloudFox, CloudPEASS, GCPBucketBrute, Prowler, ScoutSuite, checkov, aws-cli, azure-cli, Pacu |
| Containers | kubectl, kube-bench, kube-hunter, kubescape, peirates, trivy |
| Native probes | omni_cookies, omni_authz, omni_upload, omni_race, omni_bucket_azure, omni_ws, omni_content |
⚠ ysoserial: Kali apt package unavailable at build. TeamFiltration: operator-installed per engagement.